Direct Answer
After the monitoring platform goes live, there is a pile of alarms but nobody closes them out. How should the disposition process be designed? The answer: four elements — graded thresholds (normal / attention / warning / alarm / linkage), the responsible person and response time limit for each grade, automatic work-order dispatch with closure records, and automatic escalation on timeout. The platform keeps "alarm–dispatch–disposition–review" fully recorded so every alarm has a result instead of sinking into the sea.
After an campus distribution monitoring system went live, it generated over 400 alarms in the first month. Operators were overwhelmed; repeated alarms made up 60%; nothing was closed out; hidden risks kept recurring. Redone with the four-element scheme: alarms graded into five levels (normal/attention/warning/alarm/linkage), each with a responsible person and time limit (e.g., alarm level = duty electrician, respond in 30 min, dispose in 8 h); the platform auto-dispatched, disposition was filled back, and timeouts auto-escalated to the supervisor. One month later, repeated alarms dropped 80%; every alarm had a closure record; the closure rate exceeded 95%. The core of an alarm-disposition scheme: grading separates priorities, responsible persons give everything an owner, closure records give every item a result, and escalation keeps the loop unbroken.
Because:
- No grading = no priority: all alarms at one level; the operator does not know what to handle first; - No responsible person = nobody owns it: an alarm with no owner recurs with nobody managing it; - No closure record = no loop: disposition not filled back makes alarms untraceable and problems "invisible"; - No escalation = no safety net: no mechanism intervenes on timeout; critical alarms can be drowned out.
Key insight: an alarm-disposition scheme solves management closure, not alarm technology. Grading, responsibility, closure, escalation — with all four, alarms have results.
At one plant, a night alarm (busbar temperature, warning level) was not responded to by the duty electrician within 40 minutes; the system auto-escalated to the supervisor with a phone call; the supervisor coordinated and completed disposition with closure within 2 hours. Without the escalation mechanism, that alarm might have waited until the next day — 8 hours of sustained high temperature, risks compounding. Automatic timeout escalation is the loop's safety net, keeping alarms from being drowned out at night.
1. Graded Thresholds and Response-Time Table
Step one: how alarms are graded and time limits set.
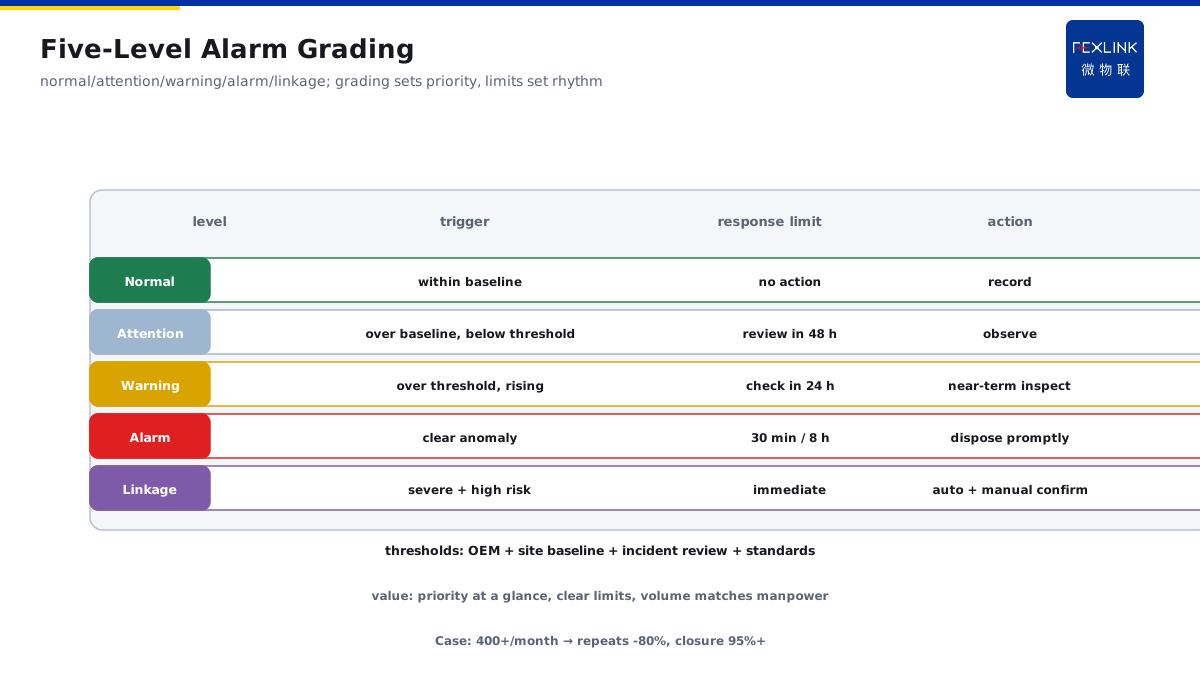
Five-level alarm definition: - Normal: data within baseline; no attention needed; - Attention: over baseline but below threshold, stable trend — record and observe; - Warning: over threshold with rising trend; near-term inspection needed (e.g., 24–72 h); - Alarm: clear anomaly; dispose promptly (e.g., respond in 30 min, dispose in 8 h); - Linkage: severe anomaly with high risk; automatic linked disposition (e.g., trip, fire-fighting activation, shedding non-critical load).
Where graded thresholds come from: - OEM recommended values (temperature, PD, leakage thresholds); - On-site baseline measurement (background noise, normal fluctuation range); - Historical incident review (precursor values before incidents); - National standards / procedures (follow the regulation where one exists).
Response-time table: - Attention: review within 48 h (record and observe); - Warning: on-site check within 24 h; - Alarm: respond in 30 min, dispose in 8 h (duty electrician); - Linkage: dispose immediately (auto linkage + manual confirmation).
Meaning of grading: - Operators see priority at a glance (which to handle first); - Response time limits are clear (no delay, no misjudgment); - Alarm volume matches manpower (no longer one pot of everything after grading).
Key insight: graded thresholds are the priority ruler. Five-level definition + threshold sources + response limits — priority and rhythm are clear the moment an alarm arrives.
2. Responsible-Person Matrix
Step two: who gets the alarm. Responsibility lands on a person:
Responsible-person matrix design: - Each alarm type defines a responsible role (job-level): - Temperature/PD/leakage alarm → duty electrician / inspector; - Electrical-fire alarm → duty electrician + fire linkage (double confirmation); - System/communication alarm → platform administrator; - Linkage-disposition alarm → shift leader / supervisor (command decision); - Backup responsible person (takes over when the primary is absent); - Contact methods (phone + platform message).
Matrix elements: - Alarm type (temperature/PD/leakage/fire/communication); - Responsible role (who disposes); - Response time limit (how fast to respond); - Disposition authority (what they can do: inspect/isolate/de-energize); - Reviewer (who checks disposition quality).
Dispatch logic: - Platform auto-matches the responsible person by alarm type (auto dispatch); - Responsible person accepts the order (confirm receipt); - Timeout without acceptance → backup/escalation (auto flow); - Disposition complete → reviewer confirms (quality gate).
Meaning of the matrix: - Everything has an owner (every alarm has a home); - Independent of personal experience (job-based; the post remains when the person leaves); - Dispatch is automated (operators miss nothing).
Key insight: the responsible-person matrix is the ownership ruler. Type → role → time limit → authority → review, five elements define responsibility — every alarm has an owner.
3. Work-Order Flow Process
Step three: how alarms flow. The work order is the closure carrier:
Work-order flow: - Platform alarm → auto-generate work order (with alarm data); - Work order dispatched → responsible person accepts (confirm receipt); - On-site disposition → record actions (inspect/handle/replace); - Result filled back → disposition result, photos, data uploaded; - Review and closure → reviewer confirms; work order closed.
Work-order content design: - Alarm info: type, location, value, time; - Disposition guidance: suggested actions (inspect/isolate/de-energize); - Responsibility info: responsible person, time limit, contact; - Result records: process, result, residual risk; - Timestamps: alarm–accept–dispose–closure full timeline.
Flow principles: - Every step has a timestamp (fully traceable); - Every step has an owner (no break in the flow); - Disposition results are retained (review sees them); - Not closed until closed out (problems do not go "invisible").
Meaning of the flow: - Alarms are visible from "issued" to "closed"; - Recurring problems have evidence to check; - Management closure (no more sinking into the sea).
Key insight: the work-order flow is the closure carrier. Alarm → dispatch → disposition → review → closure, five steps — each with a stamp, an owner, and a trace.
4. Timeout Escalation Rules
Step four: what if nobody handles it. Escalation is the safety net:
Timeout escalation rules: - Response timeout (e.g., alarm level not accepted in 30 min) → escalate to the responsible person's superior; - Disposition timeout (e.g., not complete in 8 h) → escalate to the supervisor; - Consecutive timeouts → escalate to higher levels (shift leader → supervisor → department head); - Escalation channels: platform message + SMS + phone (multi-channel reach).
Escalation trigger conditions: - Acceptance timeout (auto-detected); - Disposition timeout (deadline passed without closure); - Re-measurement failed (data still abnormal after closure); - Linkage alarm (immediately escalate to the shift leader).
Effect of escalation: - Critical alarms are not drowned out (safety net engages); - Responsibility is enforced (timeout = accountability issue, forcing response); - Management visibility (escalation records = management evidence).
Escalation notes: - Reasonable escalation thresholds (not hypersensitive, not sluggish); - Escalation records retained (time, level); - The original responsible person still follows up after escalation (no abdication).
Typical linkage-disposition scenarios: - Busbar-temperature linkage level: auto-shed non-critical load (protect critical load) + notify the shift leader; - Electrical-fire linkage level: auto-activate fire alarm + isolate the faulty circuit + double confirmation (on site + platform); - Cable-trench flooding linkage level: auto-start the drain pump + water-level alarm + warning linkage; - Manual review is mandatory after any linked action (an automatic action ≠ a solved problem; confirm on site); - All linkage actions are recorded (when, which device, which action) for later review.
Key insight: timeout escalation is the loop's safety net. One level up on response timeout, one level up on disposition timeout — alarms are never drowned out at night.
5. Using Closed-Loop Data for Review
Step five: what comes after closure. The data must be reviewed:
Review dimensions: - Alarm distribution: type/location/period (where the hotspots are); - Repeated alarms: repeat count at the same point (problems not cured); - Disposition duration: average alarm-to-closure time (response efficiency); - False-alarm rate: share confirmed as non-defect (threshold reasonableness).
Review methods: - Weekly/monthly reports: closure rate, average disposition time, repeated-alarm TOP 10; - Trend analysis: alarm-volume trend (rising = aging equipment / unreasonable thresholds); - Root-cause analysis: repeated-alarm causes (thresholds too strict? real equipment problems?); - Optimization iteration: threshold adjustment, responsible-person adjustment, process optimization.
Value of review: - Alarms turn from "noise" into "data assets" (hotspots = retrofit priorities); - Thresholds keep improving (false-alarm rate falls); - Processes keep improving (disposition efficiency rises); - Management decisions have a basis (equipment retrofit, staffing).
Review metrics: - Closure rate (target 95%+); - Average disposition duration (continuously falling); - Repeated-alarm rate (continuously falling); - False-alarm rate (target < 20%).
Alarm noise-reduction measures: - Threshold calibration: adjust per on-site baseline measurement (too strict = more false alarms); - Suppression rules: merge short-interval repeated alarms at the same point (prevent bombardment); - Condition filtering: reasonable fluctuations during load peaks / maintenance are not reported; - Grading noise reduction: attention/warning levels are only recorded, not disruptive (focus on alarm level); - Goal: bring alarm volume down to a level operators can actually handle.
Shift and handover management: - Handover: unclosed work orders are handed over face to face (no break on shift change); - Taking-over review: confirm the status of in-progress work orders (accepted/in disposition/pending closure); - Shift log: alarm-disposition situations recorded (handover has evidence); - Night-shift assurance: alarm-level response responsibility is clear (duty electrician + backup contact); - Holidays: backup mechanism (primary on leave, backup covers).
Pre/post comparison reference: - Before: 400+ alarms/month, 60% repeated, nothing closed; - After: repeated alarms down 80%, closure rate 95%+; - Disposition duration: from ~24 h average to ~6 h (escalation mechanism drives it); - False-alarm rate: from 40% to 15% (threshold calibration + suppression rules); - Key takeaway: operators shift from "overwhelmed" to "handling by level," management has evidence.
Key insight: review makes the loop run better and better. Alarm distribution, repeated alarms, disposition duration, false-alarm rate — four dimensions of review keep the loop improving.
6. Product Landing: Multi-Level Alarm Linkage Scheme
FEXLINK products bring the multi-level alarm linkage scheme to the field:
- ESF Electrical Fire Monitor: temperature/leakage/electrical-fire monitoring, graded alarm reporting; - ESI Digital Status Monitor: switch-state/linkage-signal monitoring, linkage-disposition triggering; - Digital Electrical Intelligent Supervision System: platform alarm grading, auto dispatch, work-order closure, timeout escalation; - The platform outputs five-level alarms + the responsible-person matrix + full work-order trace; - Review reports auto-generated (closure rate, disposition duration, repeated alarms).
Design principle in one sentence: turn "alarm bombardment" into "orderly disposition closure." Grading, dispatch, closure, escalation, review — every alarm has a result.
7. Common Scheme-Design Mistakes
1. Alarms not graded: all alarms at one level. Consequence: no priority; operators overwhelmed. Correct: five-level definition + response limits. 2. No responsible-person matrix: alarms unclaimed. Consequence: recurring problems nobody manages. Correct: type → role → time-limit responsibility. 3. Disposition without closure: no fill-back after handling. Consequence: records missing; problems "invisible." Correct: work-order closure with disposition traces. 4. No escalation mechanism: nobody intervenes on timeout. Consequence: critical alarms drowned out at night. Correct: auto-escalate on response/disposition timeout. 5. Closed-loop data unused: stored but never reviewed. Consequence: alarms remain noise; thresholds unoptimized. Correct: weekly/monthly review, continuous iteration.
Scope and Limitations
This article provides an overall framework for a multi-level alarm and linked-disposition scheme for distribution systems (graded thresholds, responsible-person matrix, work-order flow, timeout escalation, closed-loop review) for disposition-process design on distribution monitoring platforms. Graded thresholds and response time limits should be adjusted to on-site equipment, staffing, and shift systems; linked disposition (tripping, fire-fighting linkage, etc.) involves safety operations and must be performed per procedures by qualified personnel with approval; escalation rules must match the organizational structure. Online monitoring data is managed uniformly through the platform to form trend alerts. All cases are anonymized (a certain campus / plant) and do not refer to any specific customer.